When our production team first started shipping pressotherapy machines to wellness chains across North America, we learned something the hard way GDPR 1. One client discovered their proprietary compression protocol settings had shown up in a competitor’s catalog. The problem? Their previous supplier had no real privacy controls Role-Based Access Control (RBAC) 2. For chain brand owners investing in custom equipment, supplier privacy protection is not optional—it is foundational.
To evaluate supplier privacy protection for chain brand pressotherapy machines, assess their non-disclosure agreements, data handling policies, security certifications like ISO 27001 or SOC 2, compliance with regulations such as HIPAA and GDPR, and their ongoing monitoring practices. Strong suppliers demonstrate contractual readiness, technical safeguards, and transparent documentation.
This guide will walk you through a practical framework for vetting your pressotherapy machine supplier’s privacy practices—from initial screening to ongoing audits. Let’s break it down step by step.
How can I ensure my proprietary pressotherapy machine designs remain exclusive to my brand?
When our engineers develop a custom pressure sequence or user interface for a client, we know that design represents months of collaboration and investment. Yet many chain brand owners worry their proprietary features could end up in generic machines sold to competitors. This fear is valid—and preventable.
To ensure proprietary pressotherapy designs stay exclusive, require suppliers to sign comprehensive NDAs before sharing any specifications, demand segregated production workflows, verify IP ownership clauses in contracts, and conduct periodic audits of manufacturing facilities. Exclusive design protection depends on contractual clarity and operational transparency.
Start with a Strong Non-Disclosure Agreement
The first line of defense is a well-drafted NDA. This document must be signed before you share any specifications, CAD files, or compression algorithms. In the context of manufacturing, a non-disclosure agreement 3 is an agreement between a manufacturer and a business or individual that legally prevents the manufacturer from revealing trade secrets 4 or other sensitive information to the public.
Your NDA should address several key elements:
| NDA Element | What to Include |
|---|---|
| Definition of Confidential Information | Design files, compression protocols, software code, branding assets |
| Permitted Use | Manufacturing only, no internal use or resale |
| Duration | Minimum 5 years, or indefinite for trade secrets |
| Return/Destruction | Requirement to return or destroy all files upon termination |
| Jurisdiction | Specify which court handles disputes |
It is important to ensure that an NDA is tailored to suit the needs of the product, but also the jurisdiction in which it is being manufactured. If your supplier is based in China, for example, the NDA should be enforceable under Chinese law.
Demand Segregated Production Workflows
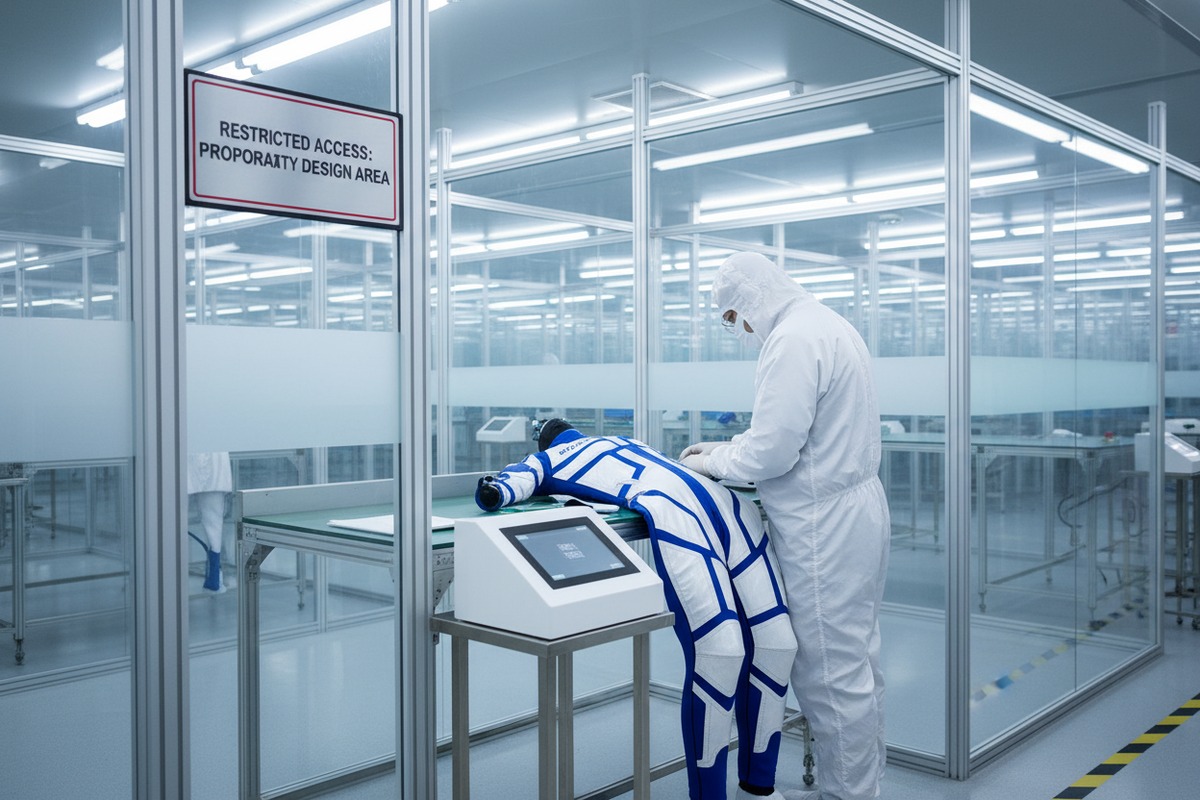
Beyond paperwork, physical separation matters. Customer branding, artwork, and product configurations are handled under strict confidentiality protocols. Production workflows are segregated to prevent cross-client exposure. Ask your supplier how they prevent one client's designs from being visible to other production teams.
Reputable manufacturers will have locked areas, separate digital file servers, and role-based access. During factory audits, verify these claims. Look for:
- Dedicated workstations for your order
- Restricted access to your design files
- Separate labeling and packaging stations
Verify IP Ownership in Your Contract
Many disputes arise from vague contract language. If the product involves collaboration between the retailer and manufacturer, the agreement should specify who owns the resulting IP and whether it can be used outside the partnership. Disputes over IP ownership can arise if these terms are vague.
Your contract should state clearly:
- You retain full ownership of all custom designs
- The supplier may not replicate or modify your designs for other clients
- Any improvements made during production belong to you
Conduct Periodic Audits
Trust but verify. Manufacturers should also conduct regular audits to ensure that retailers are adhering to these provisions and not misusing proprietary information. Schedule annual or semi-annual factory visits. Review production logs. Confirm that only authorized personnel have accessed your files.
What steps does a high-end manufacturer take to protect my chain's sensitive business information?
In our own facility, protecting client data goes beyond locking a filing cabinet. Our wellness chain partners share everything from customer demographics to site rollout timelines. If that information leaked, their competitive advantage would evaporate overnight. Serious manufacturers build privacy into their operations from day one.
High-end manufacturers protect sensitive business information through encryption, access management with multi-factor authentication, role-based access controls, incident response plans, security certifications like ISO 27001 or SOC 2, and employee training programs. These measures ensure data stays confidential throughout the supply chain.

Look for Security Certifications
Certifications are the quickest way to verify a supplier's commitment to data security. Systems and Organization Controls 2 (SOC 2 5) is a security and compliance standard created by the American Institute of Certified Public Accountants (AICPA). This framework specifies how organizations should protect customer data from unauthorized access, cybersecurity incidents, and other vulnerabilities.
ISO 27001 6 is an internationally recognized standard for establishing, maintaining, and continuously improving an Information Security Management System (ISMS).
| Certification | Best For | Geographic Strength |
|---|---|---|
| SOC 2 Type II | U.S.-based clients, SaaS, cloud services | North America |
| ISO 27001 | International clients, regulated industries | Europe, Asia, Global |
| ISO 13485 | Medical device manufacturers | Global |
| HIPAA 7 Compliance | Health data handling (U.S.) | United States |
Outside the U.S., ISO 27001 holds stronger recognition as a truly international security standard. In the EU, ISO 27001 is widely seen as the benchmark for security compliance. If your chain operates globally, prioritize suppliers with ISO certification.
Evaluate Technical Safeguards
Ask your supplier about their technical controls:
- Encryption: Are files encrypted at rest and in transit?
- Multi-Factor Authentication (MFA): The 2025 HIPAA Security Rule introduces a mandate requiring the implementation of Multi-Factor Authentication (MFA) 8 across all access points to electronic Protected Health Information (ePHI).
- Role-Based Access Control (RBAC): Only authorized personnel should access your data
- Incident Response Plans: Regular risk assessments and vulnerability scanning, incident response planning and containment strategies are essential.
Confirm Employee Training Programs
Technology alone is not enough. Employees must understand their responsibilities. Ask for evidence of security awareness training for vendor employees who handle healthcare data. This applies even if your pressotherapy machines are not classified as medical devices—the principle holds.
Request Evidence of Business Continuity
What happens if your supplier faces a cyberattack or natural disaster? Vendor assessments will evolve beyond checklists and certifications. Instead, they will examine whether a partner can support sustained patient care during a cyber event or operational failure. Ask for documentation of:
- Data backup procedures
- Disaster recovery plans 9
- Secondary facility capabilities
How do I evaluate the strength of a supplier's non-disclosure agreements for my custom equipment?
Our legal team reviews dozens of supplier NDAs each year. Some are airtight. Others have loopholes you could drive a forklift through. When your custom pressotherapy machine design is on the line, the quality of that NDA matters more than most people realize.
To evaluate an NDA's strength, review its definition of confidential information, duration of protection, permitted use limitations, return or destruction clauses, breach remedies, and jurisdictional enforceability. A strong NDA is specific, enforceable in the supplier's country, and covers both tangible and intangible information.

Key Elements to Review in Any Supplier NDA
Not all NDAs are created equal. Here is what to look for:
| Element | Strong NDA | Weak NDA |
|---|---|---|
| Definition of Confidential Info | Specific: includes designs, software, pricing, customer lists | Vague: "proprietary information" with no examples |
| Duration | 5+ years or indefinite for trade secrets | 1-2 years only |
| Permitted Use | Manufacturing for you only | Broad language allowing internal use |
| Return/Destruction | Mandatory upon termination | Optional or unspecified |
| Breach Remedies | Specific damages, injunctive relief | No specified consequences |
| Jurisdiction | Enforceable in supplier's country | Silent or only your country |
Confidential Information includes, but is not limited to, information regarding pricing, customers and prospective customers, vendors and vendor lists, costed bills of materials, processes (including but not limited to manufacturing processes), know-how, designs.
Watch for These Red Flags
When reviewing a supplier's NDA, be alert to:
- Overly broad exceptions: Some NDAs allow disclosure if information becomes "publicly known," even if the supplier caused that disclosure
- Short confidentiality periods: Most NDAs are only written to last for a period of 3 to 5 years, but they can go longer or shorter, depending on the needs of the parties involved. For trade secrets, push for longer or indefinite terms
- No mention of subcontractors: If your supplier outsources production, their NDA must bind those third parties too
- Vague breach consequences: Without specific remedies, enforcing the NDA becomes difficult
Ensure Jurisdictional Enforceability
An NDA drawn up for a U.S. manufacturer may not be legally binding in China, and vice versa. If your supplier is in China, consider:
- Drafting the NDA in Chinese and English
- Specifying Chinese courts or arbitration bodies
- Using a Non-Use, Non-Disclosure, and Non-Circumvention (NNN) agreement, which is more common in Chinese business law
Include Non-Compete and Non-Solicitation Clauses
Non-Compete Clause: This dictates a time period for which employees aren't allowed to compete with the organization. Sometimes this extends for a period after which an employee has left the company. For pressotherapy equipment, this prevents your supplier from developing a competing machine based on your specifications.
Can I trust my supplier to keep my private-label manufacturing details confidential from other distributors?
Our team has worked with chain brands who discovered their "exclusive" machine design being sold under a competitor's label. The supplier simply swapped the logo and shipped it to another buyer. This betrayal is more common than you might think—and entirely preventable with the right safeguards.
Trust in private-label confidentiality comes from verified controls, not promises. Require contractual exclusivity clauses, segregated production lines, audit rights, and evidence of how the supplier handles other clients' products. Transparency in the supplier's operations is the foundation of trustworthy private-label partnerships.
Establish Contractual Exclusivity
Through an OEM agreement, the companies can establish the nature of exclusivity of the product. For instance, will the company have exclusivity to the product for a limited amount of time, or whether the exclusivity will be limited to a certain territory.
Your private-label agreement should address:
| Exclusivity Type | Description | When to Use |
|---|---|---|
| Product Exclusivity | Supplier cannot sell this design to anyone else | You developed the design from scratch |
| Territorial Exclusivity | Supplier cannot sell to competitors in your region | You operate in a specific market |
| Time-Limited Exclusivity | Exclusive rights for a set period | Launching a new product line |
| Feature Exclusivity | Specific features remain unique to your brand | You invested in custom R&D |
Verify Production Segregation
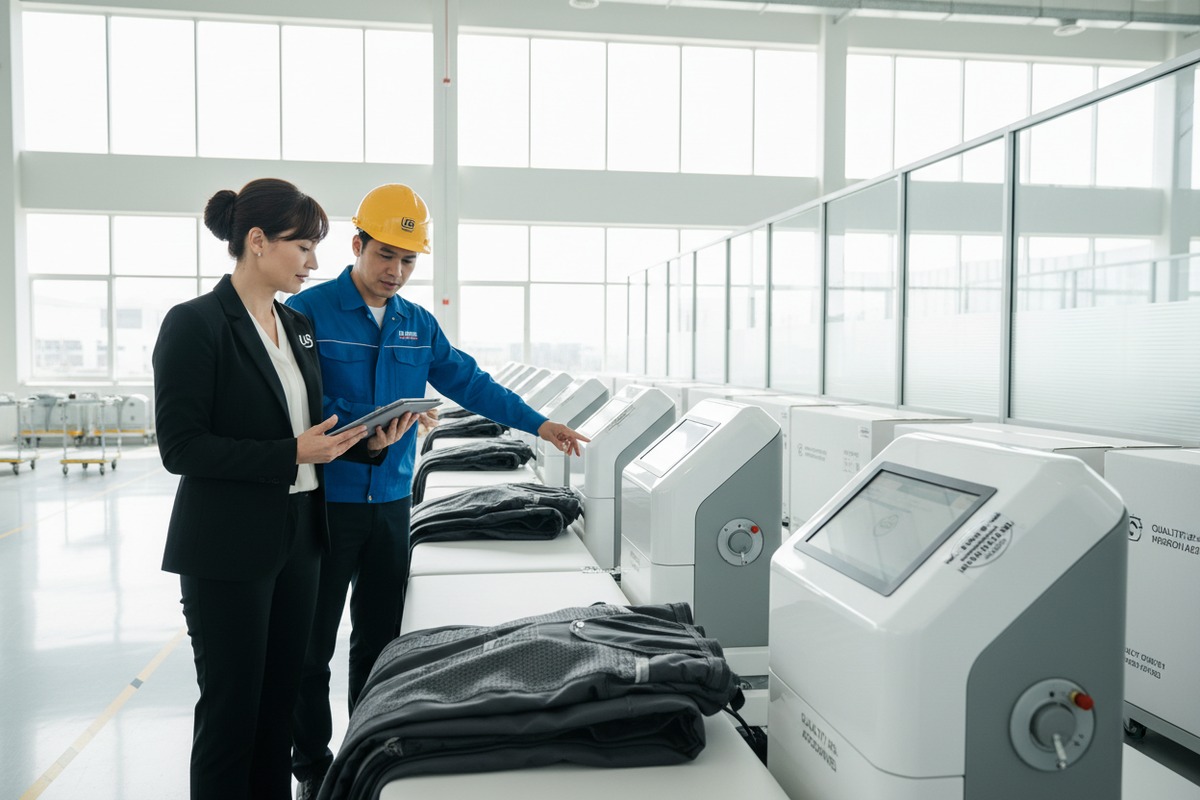
Facility means the segregated, locked, walled, restricted access space, which Supplier uses exclusively for the manufacture of the Product at Supplier's existing manufacturing facility. This level of physical separation is ideal for high-value custom equipment.
Ask your supplier:
- Are my products made on dedicated lines?
- Who has access to my production area?
- How do you prevent cross-contamination of designs?
Demand Audit Rights
Purchaser shall be permitted to inspect facilities in which the Products are developed and produced upon reasonable advance written notice. This right is essential. Without it, you have no way to verify the supplier's claims.
During audits, check:
- File access logs for your designs
- Production schedules showing your orders are segregated
- Employee rosters for your production line
Understand Data Handling for Sub-Processors
Confidentiality and Non-Compete Provisions protect proprietary information and prevent misuse by either party. But what about your supplier's own suppliers? If they outsource circuit boards or software development, your confidentiality obligations must extend downstream.
Request a list of all sub-processors and ensure they are bound by equivalent confidentiality terms.
Build Long-Term Relationships
The strongest indicator of trust is longevity. Many private-label buyers begin with a limited SKU range or pilot market. Starting with a small order allows you to evaluate the supplier's confidentiality practices before committing to a larger partnership.
Trust is earned through consistent behavior over time. Regular communication, transparent reporting, and demonstrated respect for your IP build confidence that your private-label details will remain confidential.
Conclusion
Evaluating supplier privacy protection for chain brand pressotherapy machines requires a systematic approach. Start with strong NDAs, verify security certifications, demand audit rights, and build relationships through transparency. Your proprietary designs and business information are assets worth protecting—and the right supplier will prove their commitment through documented controls, not just promises.
Footnotes
1. Offers the full official text of the General Data Protection Regulation (EU 2016/679). ↩︎
2. Explains Role-Based Access Control as a predominant model for advanced access control, as formalized by NIST. ↩︎
3. Explains the legal contract used to protect confidential information between parties. ↩︎
4. Defines trade secrets as intellectual property rights on confidential, commercially valuable information. ↩︎
5. Defines SOC 2 compliance and its criteria for managing customer data based on AICPA principles. ↩︎
6. Explains the international standard for information security management systems. ↩︎
7. Provides official information and guidance on the Health Insurance Portability and Accountability Act. ↩︎
8. Provides an official definition and explanation of Multi-Factor Authentication from NIST. ↩︎
9. Provides a definition of a disaster recovery plan as a set of procedures for organizational recovery. ↩︎

 English
 Español de México
 Deutsch
 Français
 العربية
 Русский